API Security Checklist
A 98-minute course on reviewing the security of a REST API point by point with a checklist: authentication, JWT, OAuth, inputs, responses and monitoring. Taught in Spanish.
With Daniel Alfocea
- of video
- 98 min
- videos
- 11
- level
- intermediate
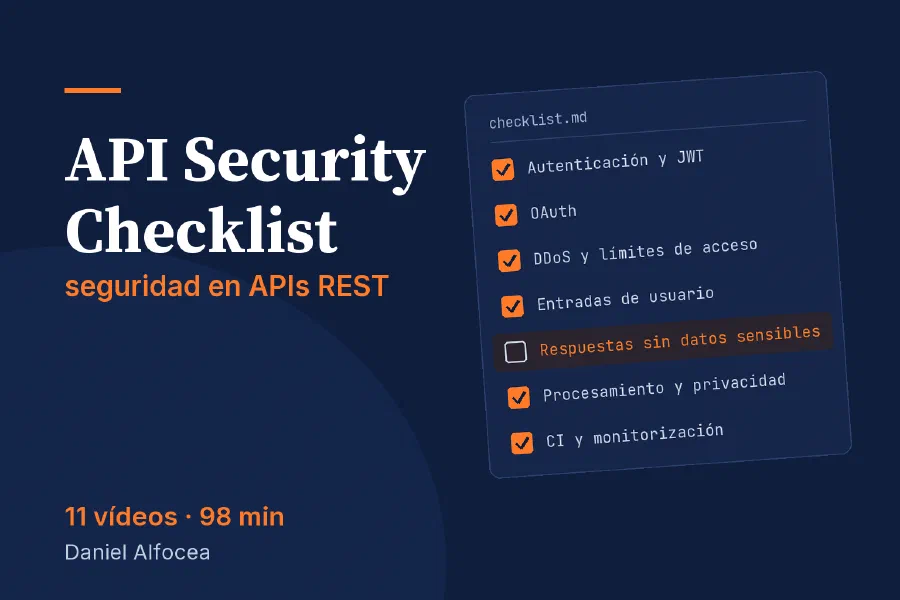
In Spanish. This program is taught in Spanish: its videos, exercises and exam are in Spanish. This page is a translation to help you decide.
Who it is for
You build or review REST APIs and want a complete security checklist to apply point by point.
About the program
Failures don’t warn anyone. A good checklist does
98 minutes of video on reviewing the security of a REST API point by point.
Language: the course is taught in Spanish. The videos and the checklist version used are in Spanish. This page is the English description only.
On January 31, 2017, GitLab was down for about 18 hours.
An engineer accidentally deleted the primary database while fixing a minor problem. And when they went to use the backups, they didn’t work as expected.
Nobody had tested the recovery routines.
It wasn’t an attack or an evil genius. It was a procedure missing one check.
APIs work exactly the same way, and almost nobody has a good checklist for their security.
Who is telling you this
I’m Daniel Alfocea. I’ve spent twenty years in development and security, and I’ve written a few audit tools (GoLismero, Plecost, Dockerscan).
Here I go through a security checklist for REST APIs with the terminal and the slides in front of me, and explain what breaks when an item is left unchecked.
I want the checklist, I'll start today
What you get
You start with the checklist and why that one, before touching a single API. What it’s for and how to use it so it doesn’t become a paper nobody opens.
Then, authentication. Which measures really matter and which are just decoration.
A whole video on JWT: how to create secure tokens and how to make life hard for an attacker.
Another on the most common OAuth mistakes and how they compromise authorization across the whole API.
Also DDoS prevention and access restrictions. How far what you can do yourself goes, and what is out of your hands.
Then you move on to data. How to secure what comes in to your API, what to do with the data once it’s inside and which attacks are waiting along the way, with privacy in the mix.
And how to respond without telling too much. The responses of a REST API say more than you think, and I show you where to look.
At the end, continuous integration and monitoring: the basic security measures, the myths going around and the danger of sensitive data exfiltration.
I won’t give away any of the reasons here. They’re all inside the videos.
What it costs
€99, one payment, and the course is yours for good.
It is not an audit, and a checklist does not replace a pentest. It’s the method that makes your APIs go through the same checks, in the same order, every time.
If you want to learn what an API is, start somewhere else.
Cheers,
Dani
P.S. If you’re unsure, watch the open lesson first. In 3 minutes you’ll know if it speaks to you.
Syllabus
98 minutes of video in 11 videos and 5 modules. The ones marked “Sample” can be watched without logging in.
01Intro y presentación 2 lessons · about 6 min
- A quien va dirigido este curso 3:14
- La checklist de seguridad de APIs que usaremos y por qué
02Autenticación y Autorización 4 lessons · about 37 min
- Medidas de seguridad en al autenticación de APIs
- JWT - cómo crear tokens seguros y ponérselo difícil a un atacante
- Prevención de DDoS y restricciones de acceso
- OAuth - Errores más comunes que comprometen la autorización
03Entradas, salidas y procesamiento seguro de información 3 lessons · about 39 min
- Securización de entradas de usuarios en APIs REST
- Procesamiento del dato, privacidad y ataques
- Respuestas de las APIs REST sin exponer información sensible
04Integración continua y monitorización 2 lessons · about 16 min
- Integración continua - medidas básicas de seguridad y mitos
- La monitorización y el peligro de la exfiltración de datos sensibles
05Contenido adicional 2 lessons
A page with the repositories and URLs I use, and the slides from the demos.
- Repositorios y URL
- Trasparencias usadas para las demos
Sample lessons
Watch them before you pay.
-
A quien va dirigido este curso3:14
Who teaches it
Daniel Alfocea
Twenty years in development and security, and author of tools such as GoLismero, Plecost and Dockerscan.
Questions
What level do I need?
Intermediate. You build or review REST APIs and know what a token, an endpoint and a header are.
If you haven’t worked with an API yet, this course will be too much for you.
Which checklist is used?
A public, open one: Shieldfy’s API Security Checklist on GitHub, in its Spanish version.
The resources lesson gives you the link, plus JWT.io and a key generator for JWT, so you can repeat the demos yourself.
Is there anything I can download?
Are 98 minutes worth €99?
It’s a checklist you’ll apply to your own APIs, and you buy it once.
And if you’re not sure, the first lesson is open. It’s 3 minutes and costs nothing.
Will my APIs come out hardened?
No. A checklist does not replace an audit or a pentest.
What you get is a method for reviewing your APIs in order, so the basics don’t slip through.
Who it is forYou build or review REST APIs and want a complete security checklist to apply point by point.