First steps with Scapy
A 144-minute course on building, sending and capturing network packets with Python and Scapy. For people who already open Wireshark and now want to make their own traffic. Taught in Spanish.
With Daniel Alfocea
- of video
- 144 min
- videos
- 24
- level
- intermediate
In Spanish. This program is taught in Spanish: its videos, exercises and exam are in Spanish. This page is a translation to help you decide.
Who it is for
You work in networking, security or development, already open captures in Wireshark and want to learn to build and send the packets yourself. You need an intermediate level of Python.
About the program
Stop looking at packets and start making them
144 minutes of video on building, sending and capturing network packets with Python and Scapy.
Language: the course is taught in Spanish. The videos are in Spanish. This page is the English description only.
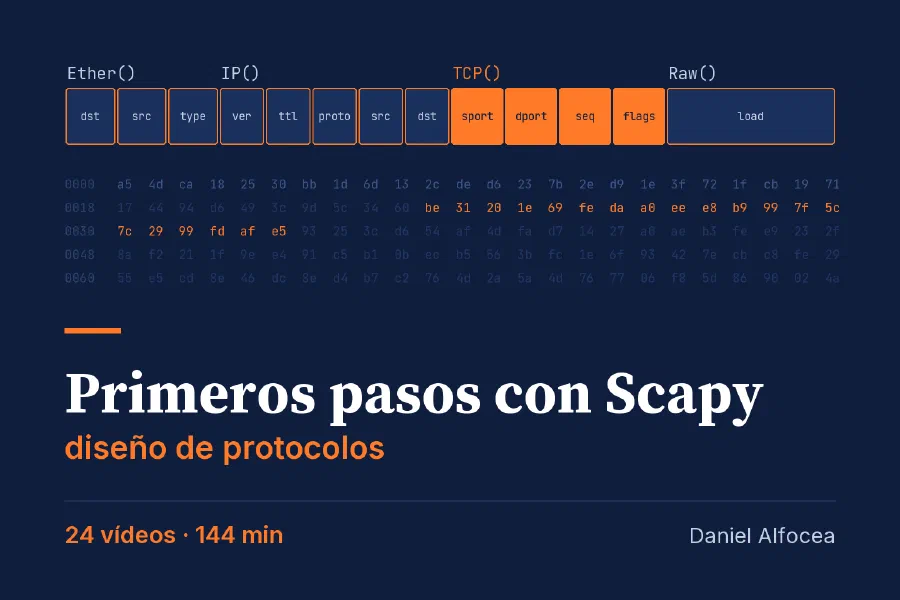
You open Wireshark, see a TCP packet and more or less understand it.
Until you have to build it yourself. With the layer you want, the fields you want, and send it to see what the other side answers.
That’s where most people end up staring at the screen.
Scapy is a Python library that does exactly that: you build the packet field by field, send it, and keep the response in a variable.
Who is telling you this
I’m Daniel Alfocea. I’ve spent twenty years in development and security, and I’ve written a few audit tools (GoLismero, Plecost, Dockerscan).
Here I teach you Scapy the way I use it, with the terminal open and typing in front of you.
What you get
First, an installation that doesn’t eat your afternoon. Each operating system has its quirks and I cover them before sending the first packet.
Then when to send at layer 2 and when at layer 3, and which of the two lets you control the packet field by field.
Interactive mode spits out warnings constantly. Some can be ignored and some will ruin your work, and I tell you which. Also how to turn on an autocompletion that Python doesn’t ship with.
There’s a whole module on Wireshark, tcpdump and tshark. When to reach for each one, how to save your filters as shortcuts and what a dissector does inside so Wireshark understands a protocol.
Another on capturing with sniff, parameter by parameter. Including the one that makes the capture stop on its own when it sees what you were looking for.
And at the end you write two tools of your own: a DNS fuzzer and a two-thread program, one sending ICMP and the other listening for the reply.
I want to build my own packets
What it costs
€89, one payment, and the course is yours. If I update it, you get the new version without paying again.
You won’t come out a protocol expert, that takes years. You come out with a solid base and two programs you can open, break and change.
If you already know how to send packets with Scapy, modules 1 to 3 are not for you.
Cheers,
Dani
P.S. If you’re unsure, watch the three open lessons first. In 13 minutes you’ll know if it’s for you.
Syllabus
144 minutes of video in 24 lessons and 6 modules. The ones marked “Sample” can be watched without logging in.
01Introducción 2 lessons · about 7 min
- ¿A quién va dirigido este curso? 3:21
- Qué es Scapy y por qué es mejor que otras alternativas
02TL;DR - Conceptos básicos 3 lessons · about 14 min
- Instalación
- El modelo OSI y TCP/IP 5:46
- Compatibilidad entre protocolos 3:53
03Primeros pasos con Scapy 5 lessons · about 43 min
- El modo interactivo de Scapy
- Enviando el primer paquete
- Enviando y recibiendo información (Parte 1)
- Enviando y recibiendo información (Parte 2)
- Funciones útiles
04Wireshark como navaja suiza 3 lessons · about 22 min
- Introducción a las herramientas- Wireshark, tcpdump y tshark
- Trabajando con Wireshark
- Disectores en Wireshark
05Interceptando tráfico 7 lessons · about 35 min
- Introducción
- La función sniff
- El parámetro FILTER
- El parámetro LFILTER
- El parámetro STOP_FILTER
- El parámetro PRN
- El modo offline
06Scripting con Scapy 4 lessons · about 23 min
- Introducción al Scripting con Python y Scapy
- Creando un script básico con Scapy
- Creando una herramienta completa
- Trabajando con hilos en Scapy
Sample lessons
Watch them before you pay.
-
¿A quién va dirigido este curso?3:21
-
El modelo OSI y TCP/IP5:46
-
Compatibilidad entre protocolos3:53
Who teaches it
Daniel Alfocea
Twenty years in development and security, and author of tools such as GoLismero, Plecost and Dockerscan.
Questions
How much Python do I need?
An intermediate level. You can write a script, use functions and read a traceback without panicking.
The course is about networks, not programming. If you’ve never written Python, you’ll be dragging from module 3.
Is it useful if I already use Wireshark or tcpdump?
Yes. It’s for you, in fact.
With Wireshark you look at what has already crossed the wire. Here you make it yourself, and on the side you understand what you see in the capture much better. One whole module covers Wireshark, tcpdump and tshark: when to use each.
Linux, macOS or Windows?
What do I send the packets to?
To your own things. The examples send ICMP packets and fuzz a DNS server, and that is tested against a machine you control or have permission to test.
Sending this at someone else’s network is not part of what I teach.
Are 144 minutes worth €89?
If they save you an afternoon fighting the installation and the warnings in interactive mode, they’ve already paid for themselves.
And if you’re not sure, start with the three open lessons. They’re 13 minutes and cost nothing.
Will I come out knowing everything about Scapy?
No. It’s recorded as an introduction: install, send, capture and write two small tools.
With that you have the base to continue on your own with Scapy’s documentation, which you also learn to consult from the console itself.
Who it is forYou work in networking, security or development, already open captures in Wireshark and want to learn to build and send the packets yourself. You need an intermediate level of Python.